International Standards for Secure Hardware Destruction
International Standards for Secure Hardware Destruction
A retired server can still hold customer records. A damaged laptop drive can still contain financial files. Before equipment leaves your business, you need to decide how to remove its data and how to prove that the process worked.
International standards for secure hardware destruction help you make those decisions. But they cover different things. Some guide data sanitization. Others cover information security, destruction equipment or responsible electronics recycling.
Understanding the rules for hard drive destruction means knowing which requirement applies to your device, your data and your disposal plan. A certification logo alone does not answer those questions.
read more: hardware destruction
Which Standards Apply to Hardware Destruction?
The table below explains the main references and what to check when reviewing a disposal provider.
These references complement each other. A business may use ISO 27001 to manage information security, NIST to guide its sanitization programme, and a technical standard to select the treatment method.
International Standards for Secure Hardware Destruction

NIST SP 800-88: A Framework for Data Sanitization
Businesses searching for nist standards for hardware disposal usually mean NIST SP 800-88, Guidelines for Media Sanitization. Revision 2 replaced Revision 1 in September 2025. It defines three sanitization methods:
Clear: protects against recovery through the normal device interface.
Purge: makes recovery infeasible using advanced laboratory techniques and can allow reuse.
Destroy: makes recovery infeasible and prevents further use of the storage medium.
Revision 2 focuses on managing the sanitization programme. It refers to IEEE 2883, NSA specifications or an organisation-approved standard for most technique details. For your disposal project, ask the provider to name the selected method. Avoid accepting “secure hard drive wiping” as the whole explanation. Your team needs enough detail to approve the work and review the results.
our services: hard drive degaussing service
HMG IS5: UK Secure Sanitization Requirements
HMG Information Assurance Standard No. 5, commonly called IS5, remains a reference in some UK government disposal requirements. If a customer or contract names it, confirm the exact policy and service requirements before choosing a treatment.
The UK National Cyber Security Centre also publishes guidance on secure sanitization and disposal of storage media. Its public guidance addresses risks associated with OFFICIAL information. It directs organisations handling SECRET information or above to separate guidance.
For businesses, the practical point is to check the information classification and the device type. An overwrite profile named in an older policy should not become the default treatment for every storage device.
IEEE 2883: Technical Requirements for Storage Sanitization
You may see older articles refer to IEEE P2883. The published standard is IEEE 2883-2022. It specifies methods for sanitizing logical and physical storage, with technology-specific requirements and guidance.
For example, ask your provider to separate:
Magnetic hard disk drives.
Solid-state drives.
Removable storage.
Equipment with built-in storage.
You must request a clear explanation of the method proposed for each group. Our recommendation is to settle those details before comparing prices. A low quotation offers little value if the proposed process does not meet your disposal policy.
ISO/IEC 27001: Managing Information Security
The search phrase iso 27001 hard drive destruction can suggest that ISO 27001 specifies a shredding technique. It actually sets requirements for an information security management system. Secure disposal belongs within that broader system. Your organisation should understand its risks and establish suitable controls.
A practical disposal procedure should answer questions such as:
Who approves equipment release?
Where does the team store assets before collection?
Who can access them?
How does the business approve the treatment method?
Who checks the provider’s final report?
How does the team handle missing items?
When choosing a provider, review its certificate scope and ask for its disposal procedure. The certificate and procedure provide different evidence. You need both to understand how the service will work.
ISO/IEC 27040: Protecting Storage Throughout Its Life
ISO/IEC 27040:2024 covers storage security. Its scope includes devices, media and related management activities during use and after the equipment reaches the end of use or end of life. It covers more than the timing of data sanitization. For a business, this means planning disposal while the equipment is still part of the asset inventory.
Moreover, your team should identify the storage devices, decide which assets may leave the organisation, and agree on treatment before the collection date. Leaving these decisions until equipment reaches the loading area can create confusion. Early planning gives IT, operations and compliance teams time to resolve exceptions.
ISO/IEC 21964: Physical Destruction of Data Carriers
The correct name is ISO/IEC 21964. The series was published in 2018 and incorporates the content of Germany’s DIN 66399. It covers destruction principles, equipment requirements and the destruction process.
When discussing physical destruction, ask the provider to identify:
The applicable media category.
The proposed security level.
The required destruction output.
How it will check that output.
Be careful with tables that list fragment sizes without explaining the units. A measurement in square millimetres describes the area. It is different from a measurement in millimetres, which describes length.
read more: shredding vs. degaussing for secure data destruction
What About Legacy DoD Requirements?
Some customer policies still mention dod hard drive destruction standards. In commercial discussions, this often refers to older DoD 5220.22-M overwrite patterns.
NIST Revision 2 identifies the older requirement for a fixed number of overwrite passes as obsolete. A “DoD wipe” claim alone therefore does not establish that a service suits modern storage.
If your contract names a defence requirement, confirm the exact obligation with the responsible security authority. NSA publishes separate requirements for hard disk destruction devices, magnetic degaussers and solid-state destruction equipment.
Implementing Secure Hardware Destruction
To comply with these international standards businesses should follow a structured approach to hardware destruction:
Developing Policy: Develop a clear policy on the disposal of hardware and destruction of data according to international standards.
Choose Certified Vendor: Work with vendors certified in standards such as R2 or e-Stewards, ensuring that your hardware gets destroyed securely and responsibly.
Documentation and Verification: All hardware destroyed, including the certificates of destruction by the vendors, will be documented in minute detail to meet international standards of destruction.
Regular Training: All the staff involved in the disposal process should be trained regularly, and they should be equipped with the latest safe destruction of hardware information and international standards.
Other articles: Policy and Laws Around E-Waste
What are the main approaches to hardware destruction?
Ensuring that hardware destruction is carried out properly guarantees that data cannot be recovered from destroyed devices. Ensuring impacts on the environment is two major considerations. The destruction of hardware is usually done by some basic methods to ensure that the data does not fall into anybody's hands. Here's a look at the primary strategies:
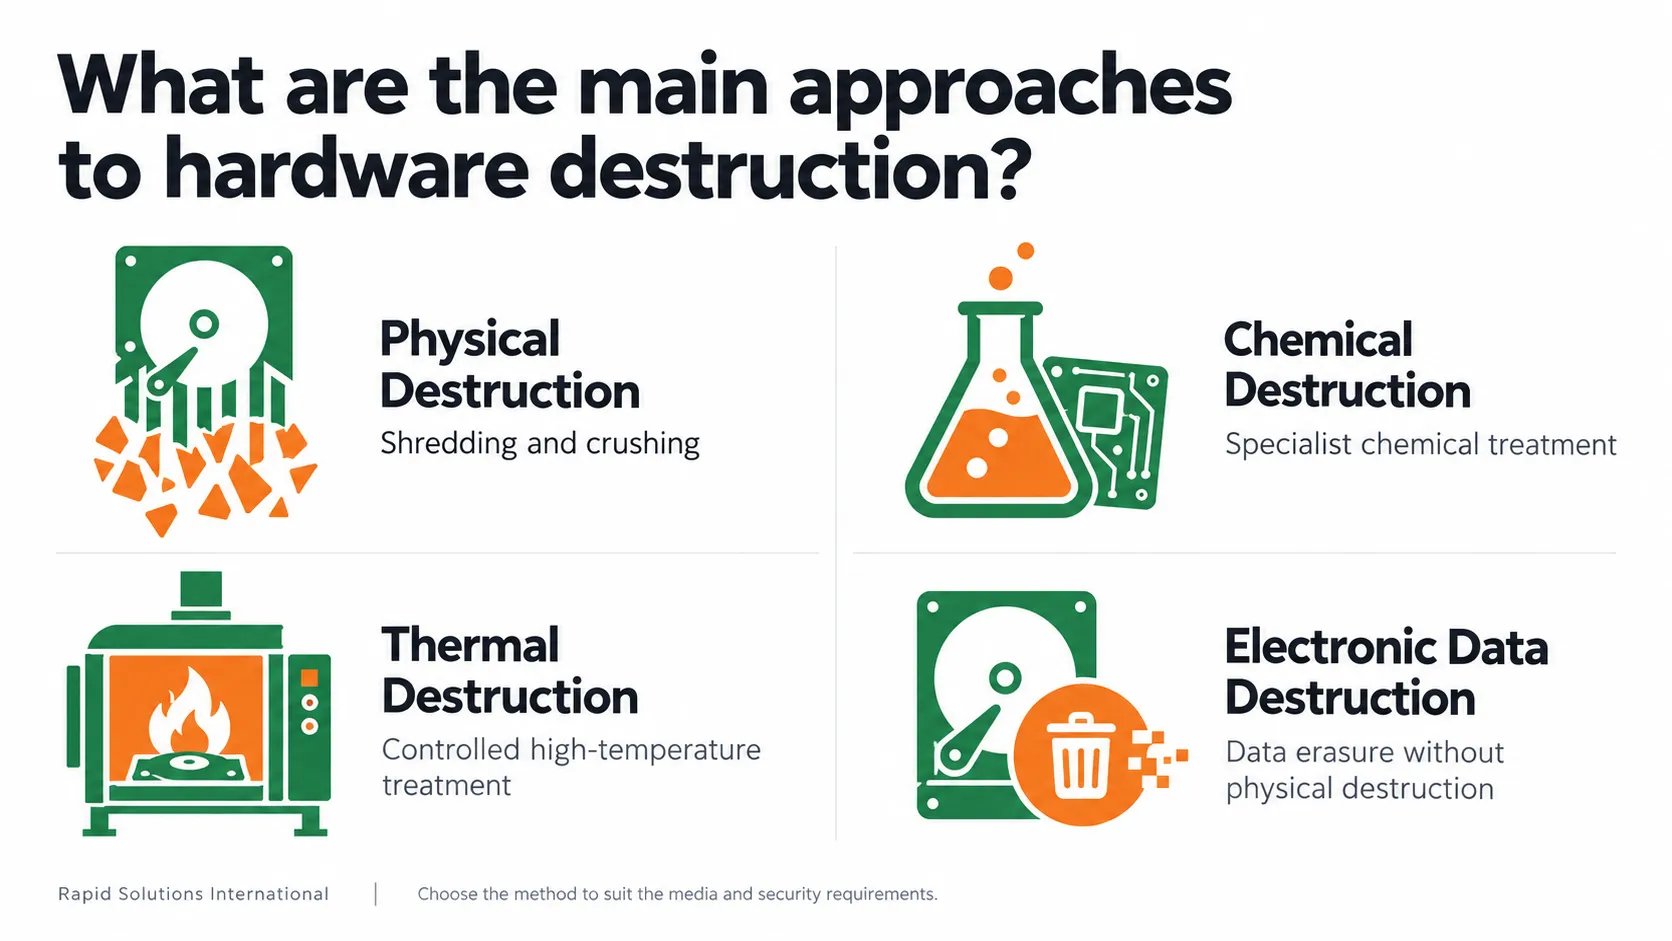
Physical Destruction
- Shredding: A shredder works much like a paper shredder but much more powerful, able to tear hard drives, smartphones and similar devices to bits from which data recovery is not possible.
Crushing—this means a device using hydraulic pressing or crushing with a hammer to physically destroy the gadget; hence, all the internal parts and mechanisms of data storage are made non-repairable.
- Drilling and Degaussing: In drilling, it physically creates holes in the structure of the storage devices to destroy it. Degaussing, on the other hand, takes all data into an irrecoverable state by disrupting the magnetic field of the data storage device through some strong magnets.
read more: do hdds degrade over time
Chemical Destruction
- Acid Bathing: Some chemicals within corroding and dissolving electronic components destruct the hardware and information contained in them. Great care is needed in the way the chemical is handled and disposed of since it may lead to environmental damage.
Thermal Destruction
- Incineration: Exposing the hardware to high temperatures, possibly using special incinerators, in order for the component part of the hardware to melt or vaporize and thus guarantee destruction of the data. The method is doable but some application should be under control, laying limits on the emission of toxic elements.
Electronic Data Destruction
- Overwriting: This is the method done whenever the data is being written over the existing data repeatedly until a point where the original is completely obscured and hence rendered unobtainable anymore.
- Encryption and Data Wipe: The data may become inaccessible through the process of first encrypting and later wiping the key of encryption. Data Overwrite: Overwriting the data by software-based wiping methods can be used. The necessity for higher security needs physical destruction and is often recommended.
Other articles: Are Hard Drives Hazardous Waste?
Secure Hardware Disposal With Rapid Solutions International
Rapid Solutions International provides on-site and off-site data destruction, data erasure, shredding, degaussing, asset serialization and reporting in the UAE. To plan your project, share your asset list, storage types, location and security requirements with our team. Ask us to confirm the proposed treatment and reporting before work begins.
Learn more about our hard drive destruction service and data destruction services.
Conclusion
Following the international standards in the disposal of your old computers and tech gear is much more than ticking the boxes for compliance. This really comes down to making sure that private and important information stored on these devices is fully protected once it is no longer needed. But more than that, it is the commitment to the care of our planet. The adoption of these standards by the business, at a minimum, protects against possible risks like data theft or harm to the environment from incorrect hardware disposal. They're actively playing a part in creating a safer, greener future.
FAQs
1. Which Standard Should My Business Follow?
Start with your contractual obligations, security policy and storage types. Ask your provider to explain which references apply and how the proposed service meets your requirements.
2. Does ISO 27001 Certification Prove That Each Drive Was Destroyed Correctly?
No. It covers an information security management system. You can review the certificate scope and request records for your specific disposal project.
3. Can Degaussing Remove Data From an SSD?
No. Degaussing does not sanitize non-magnetic flash storage. The provider must select a suitable treatment for the device.
Ask an Expert
Call us 24/7 or submit the form below to speak with one of our specialists.
All fields required